Japan’s SCS assessment scheme
METI is building a supply chain security assessment scheme. Expect more customers to ask suppliers to demonstrate their security posture.
Continuous Security Assurance (CSA)
Pipeline uses scan-based external evidence to continuously show the cyber risk of your organisation, subsidiaries, contractors and suppliers — from SCS readiness and executive and audit reporting to first-response incident investigation.
Japan Security Awards: 2024 Grand Prize · 2025 Excellence Award
Organisations we work with
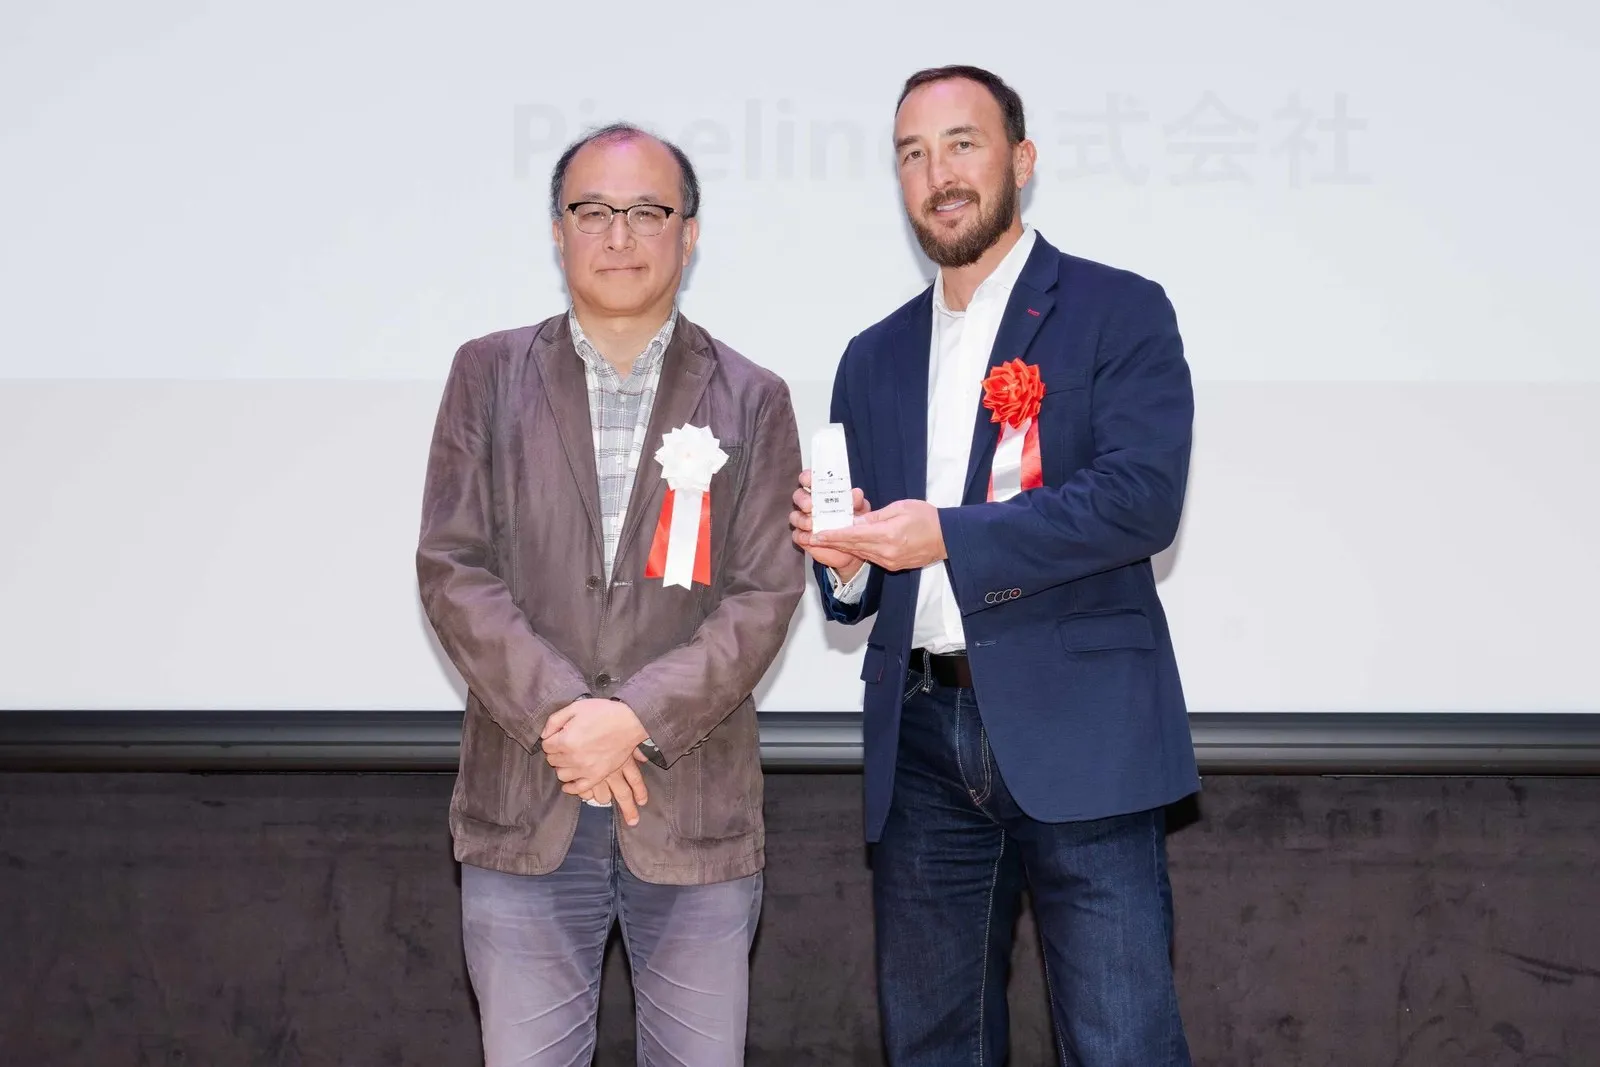
Japan Security Awards 2025Excellence Award
For RiskSensor ASM, which combines AI with expert insight.
Official winners list(opens in a new tab)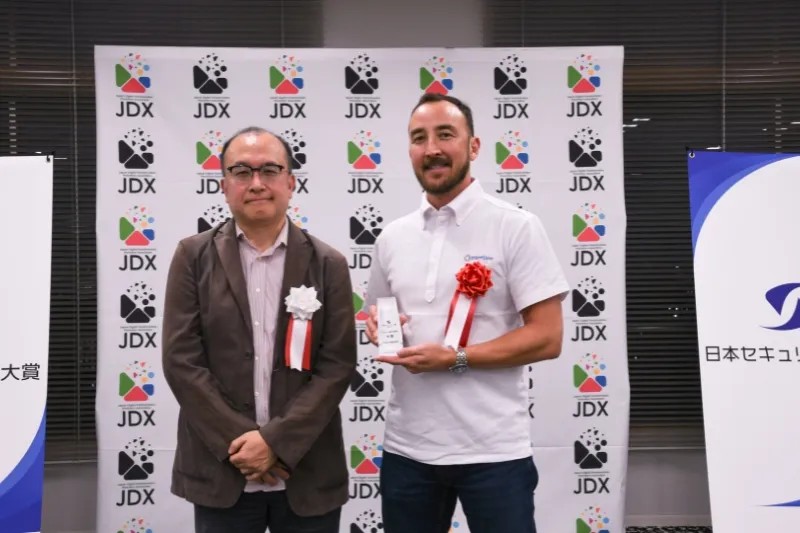
Japan Security Awards 2024Grand Prize
For our proprietary cyber intelligence technology.
Official winners list(opens in a new tab)Interop Tokyo Best of Show Award 2022Winner, Security category
DatalaiQ, our platform for securely collecting, storing, analysing and visualising machine data, was selected as a finalist and named a winner.
Official winners list(opens in a new tab)WHY NOW
METI is building a supply chain security assessment scheme. Expect more customers to ask suppliers to demonstrate their security posture.
Self-attested questionnaires and annual reviews capture a single moment. They miss configuration changes and new vulnerabilities.
Subsidiaries and contractors outside your direct control can become the entry point for an attack.
RiskSensor SCS
From your company out to tier-one, tier-two and tier-three suppliers. Continuous external checks show at a glance where risk sits and what is already verified.
Explore RiskSensorHOW IT WORKS
We collect and connect scattered external data, then prioritise it by business impact so it supports decisions and action.
01 OBSERVE
Domains, IPs, DNS, vulnerabilities and dark-web data, collected continuously.
02 CONNECT
Map findings to you, group companies, contractors and suppliers.
03 PRIORITIZE
Weigh asset importance, blast radius and exploitability.
04 ASSURE
Reports executives, auditors and partners can rely on, with progress tracked over time.
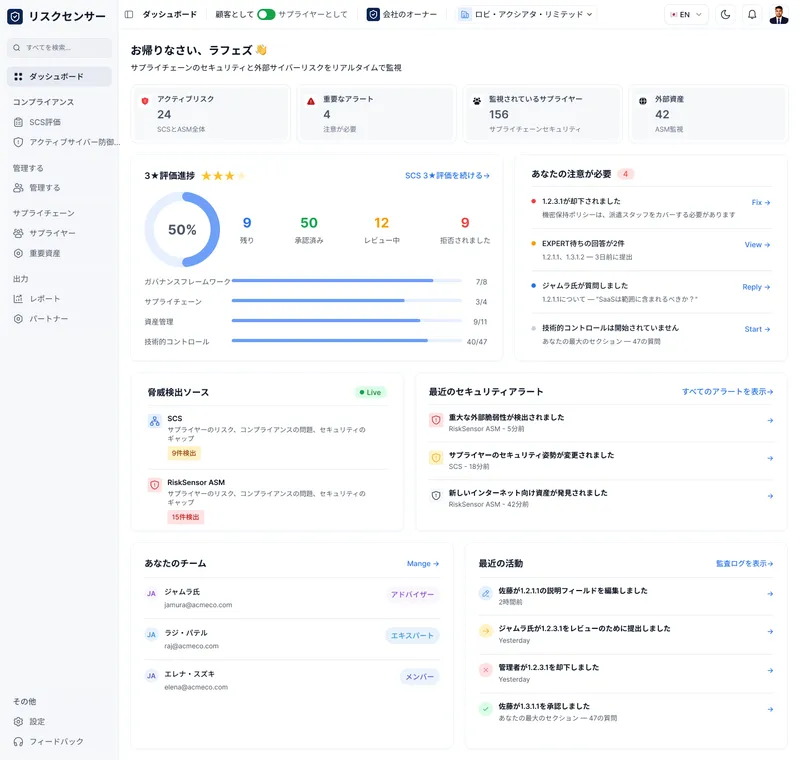
RiskSensor
See changes in external risk from ERI alongside SCS assessment and remediation status, and keep repeating “check risk → assess and act → re-check”.
Explore RiskSensorFLAGSHIP PLATFORM · PATENT PENDING
Don’t stop at a one-off assessment. RiskSensor connects externally visible risk with your internal controls, so you and your suppliers can keep verifying and improving security as things change.
Share the domains you want checked and we show you an overview of your externally visible risk.
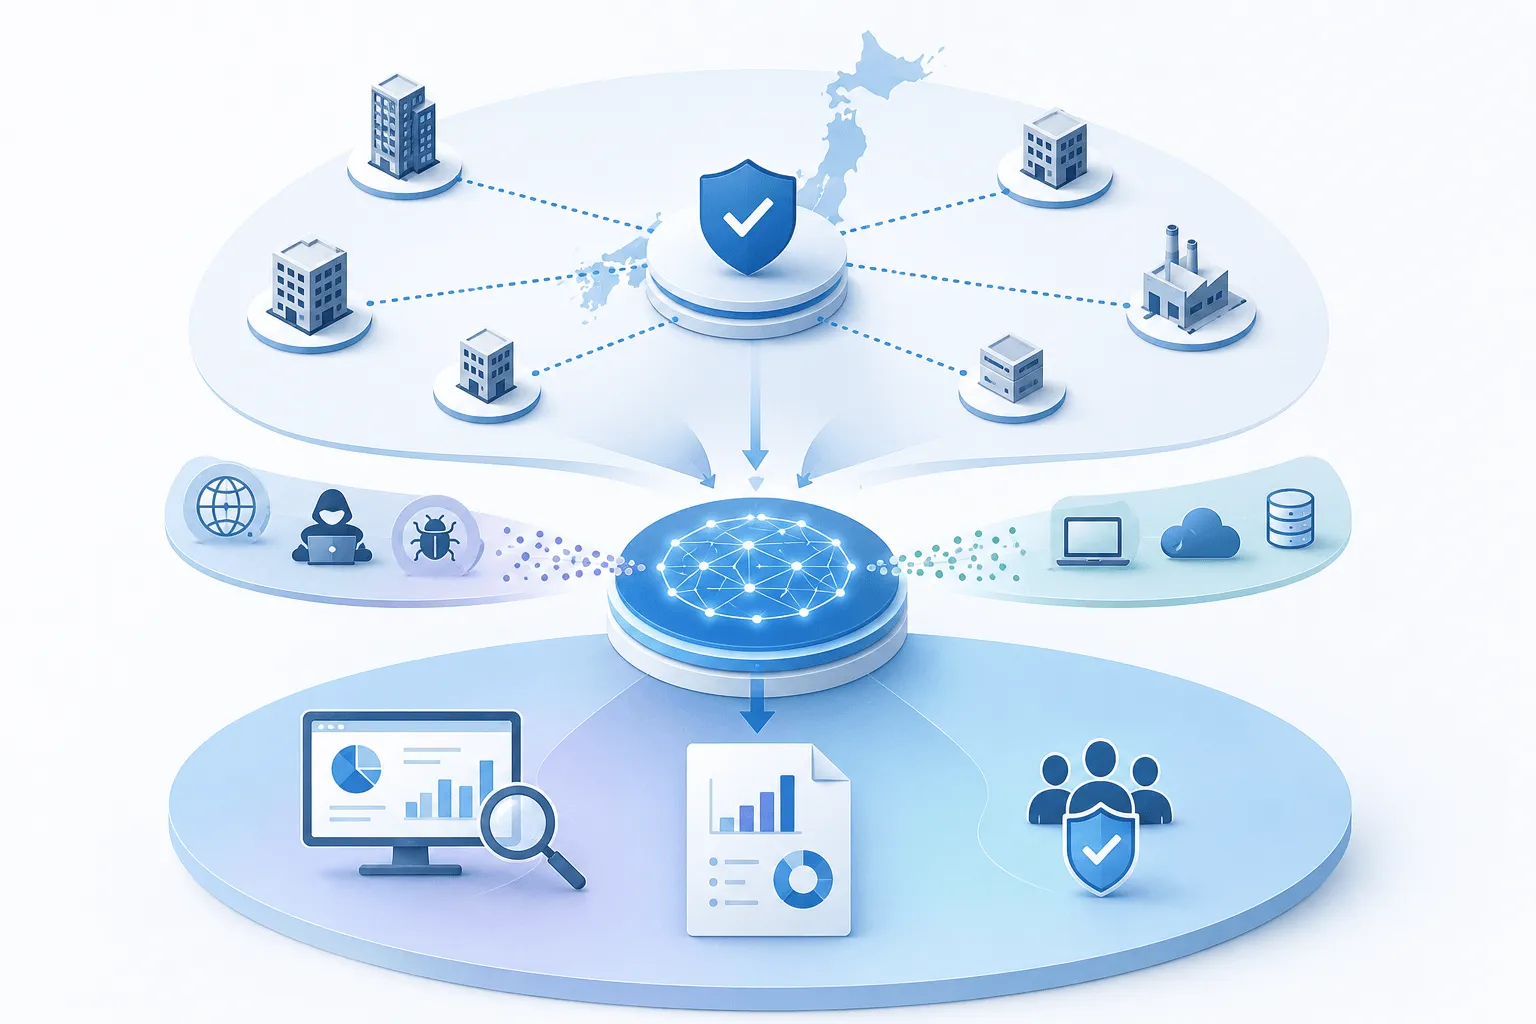
Starting from a domain, continuously check internet-facing assets, vulnerabilities, misconfigurations and signs of leaked data.
Support for Japan’s SCS assessment scheme, from questionnaire answers and evidence review to gap identification and remediation tracking.
Threats relevant to you as objective external intelligence, fed via API into DNS, firewalls, SIEM and your other defences.
Catch early signs of vulnerabilities before they are exploited, and prioritise what attackers are actually exploiting in Japan, with evidence.
Know where you stand and be ready to explain it to customers.
Keep watch on the external risk of key suppliers and contractors.
Find unmanaged assets and misconfigurations the way attackers do.
Turn findings into reports for the board and auditors.
Feed relevant threat intelligence into DNS, firewalls, SIEM and other existing defences.
AI-assisted log analysis plus expert review to establish what happened, with evidence.
PIPELINE
From our Tokyo headquarters, with sales in Singapore and R&D in Dhaka, we work across investigations, intelligence and product development.
About the companyINCIDENT RESPONSE
When checks or monitoring surface warning signs, Pipeline analysts investigate logs and dark-web sources and set out confirmed facts and next steps, with evidence. Contracted customers get a first response within 4 business hours (weekdays 9:00–18:00 JST; 24/7 available under an agreed SLA).
An approach that continuously assesses and reports the security posture of you and your suppliers using scan-based evidence rather than self-attestation.
A questionnaire reflects one moment and one respondent’s view. RiskSensor continuously checks externally observable facts, so you see change over time and can verify questionnaire answers.
A scheme being developed by Japan’s Ministry of Economy, Trade and Industry (METI) to assess the security measures of supply chain companies in tiers.
No. RiskSensor assesses externally observable information, so it does not require software in your suppliers’ environments.
From early research to deployment planning, our team is here to help.
Researching
Product overview, the CSA approach and how to prepare for SCS.
Download materialsWant to see your exposure
See an overview of your externally visible risk — useful for internal review and supplier conversations.
Request a quick risk checkEvaluating
Tell us about your challenges and we will recommend an approach and show you a demo.
Talk to an expertDealing with an incident right now?
Our analysts investigate logs and dark-web sources and set out confirmed facts and next steps. Contracted customers get a first response within 4 business hours (weekdays 9:00–18:00 JST; 24/7 available under an agreed SLA).