SMEs
Short on specialists and budget.
RiskSensor · Patent pending
RiskSensor makes external risk visible and keeps verifying and improving it.
Short on specialists and budget.
Hard to see across all suppliers.
Customer information is scattered.
The same checks are repeated from company to company.
Apr
Assessment
Report completed
Jun
External risk changes
Situation changes
Jul
Re-check & improve
Respond to change
Dates are illustrative.
From a one-off assessment to continuously catching change, verifying and improving.
Continuous Security Assurance
Don’t stop at a one-off assessment. Repeat external checks and assessment with evidence, catch change as it happens, and stay ready to explain where you stand.
External risk and internal controls, in one place.
External Risk Intelligence
Starting from a domain, continuously check internet-facing assets, vulnerabilities, misconfigurations and signs of leaked data.
Supply Chain Security
Support for Japan’s SCS assessment scheme, from questionnaire answers and evidence review to gap identification and remediation tracking.
Threat intelligence
Threats relevant to you as objective external intelligence, fed via API into DNS, firewalls, SIEM and your other defences.
Early Vulnerability Intelligence (roadmap)
Intelligence that catches early signs of vulnerabilities before they are exploited.
RiskSensor ERI
From a domain to its subdomains, public servers and open ports. We keep checking what is visible from outside and tell you when something is exposed.
RiskSensor ERI — External Risk Intelligence
All you need is a domain. See yourself and your related companies the way attackers and customers do: from the outside.
Discover assets linked to your domain, unnecessary ports and services, and exposed admin panels.
Known vulnerabilities (CVE), web application weaknesses and SSL/TLS settings, prioritised by risk.
Check the dark web and public sources for credentials, email addresses and other data that may already be exposed.
01 DISCOVER
Map internet-facing assets from your domain.
02 VERIFY
Check vulnerabilities, misconfigurations and leaks.
03 MONITOR
Regular checks catch what changes.
04 IMPROVE
Re-check fixes and record progress.
RiskSensor SCS — Supply Chain Security
End-to-end support for Japan’s SCS assessment scheme, from answers and evidence to remediation.
01 01
Answer the questionnaire
02 02
Organise and review supporting documents
03 03
Identify gaps and items needing review
04 04
Track owners, deadlines and status
SCS: METI’s security assessment scheme for strengthening supply chains.
Beyond self-attestation: verify against evidence, then improve.
Vision Intelligence Data
External threat intelligence narrowed to what matters to you, in a form your DNS, firewall, SIEM and other existing tools can use.
Vision Intelligence Data
Threats relevant to your organisation, delivered as objective external intelligence and tied to detection, investigation, prioritisation and response. What you need isn’t more data — it’s knowing early what applies to you, inside the defences you already run.
Malicious domains, IP addresses, attack infrastructure and related threat information.
Via API and data feeds into DNS, firewalls, SIEM, log platforms and security services.
With telecom, security, cloud and managed service providers, from service design through to operations.
Alongside our own observations, we can combine data from Censys, Spamhaus, Team Cymru and SURBL, which we resell as an authorised partner.Intelligence partners →
RiskSensor EVI — Early Vulnerability Intelligence Roadmap
Instead of treating every vulnerability the same, EVI prioritises what is actually being exploited in Japan, with evidence, so you know what to fix today.
Campaigns targeting Japan and actively exploited vulnerabilities, summarised daily in Japanese and English, each with evidence, applicability and fix.
Notified the moment exploitation is confirmed in Japan, with a suggested deadline, how to check if it applies, and how to fix it.
Delivered via API, webhook or STIX/TAXII 2.1, ready for your SIEM or threat intelligence platform.
| Generic CVE feed | RiskSensor EVI | |
|---|---|---|
| Where it looks | US-centric lists | Japan-first sources: JPCERT/CC, JVN, Japanese channels |
| What it tells you | Just severity scores | What is really being exploited — dark web, live attacks |
| What it costs you | Everything, noise and all | Only what applies to you |
Your data never leaves. No CVE lists, asset data or queries are sent to Pipeline.
Roadmap: planned capabilities, subject to change.
See changes in external risk from ERI alongside SCS assessment and remediation status on one screen, and keep repeating “check risk → assess and act → re-check”.
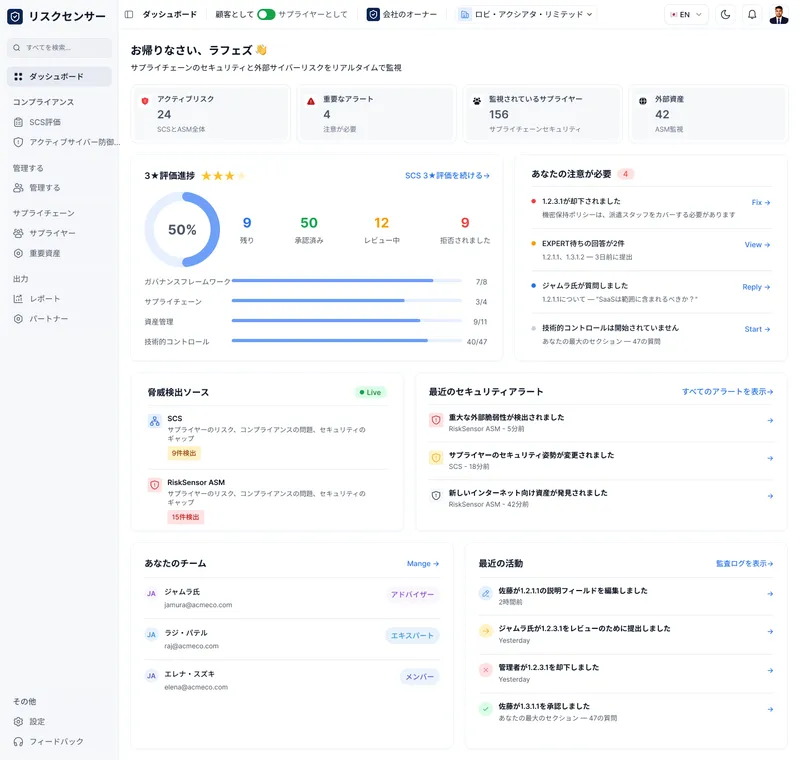
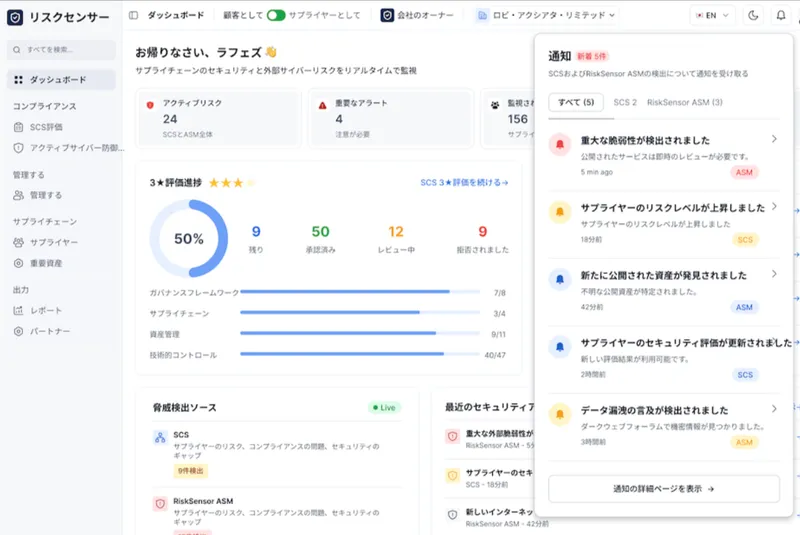
Actual product screens (demo data).
A shared workspace where companies, suppliers and experts check and improve together, sharing information safely according to permissions.
Answers, evidence, improvement
Supplier assessment and progress
Evidence review and advice
Ongoing operations
RiskSensor AI tailors its support to each user’s role.
Help answering questions, organising evidence and checking what’s missing.
Help reviewing submissions, matching evidence against gaps and speeding up assessments.
All you need is a domain. Minimal load on your systems and no prior setup.
01 STEP 1
Decide which domains (or global IPs) to check.
02 STEP 2
Run at a time that suits you. Scans finish in tens of minutes to a few hours.
03 STEP 3
An executive summary plus a detailed practitioner report, delivered within days.
04 STEP 4
We walk you through the results, then regular checks catch what changes.
INCIDENT RESPONSE
When checks or monitoring surface warning signs, Pipeline analysts investigate logs and dark-web sources and set out confirmed facts and next steps, with evidence. Contracted customers get a first response within 4 business hours (weekdays 9:00–18:00 JST; 24/7 available under an agreed SLA).
Just the domains you want checked. No software needs to be installed in your environment.
Scans finish in tens of minutes to a few hours; the report arrives within days.
Yes. It includes a summary written for non-technical executives plus practitioner detail, and can be used as evidence.
RiskSensor SCS manages the whole flow, from questionnaire answers and evidence review to gap identification and remediation tracking.
Yes. Supplier and contractor risk and remediation progress are tracked per company in shared workspaces.
Start by seeing what your organisation looks like from the outside.
See your exposure
An overview of your externally visible risk.
Request a quick risk checkResearching
The RiskSensor product overview.
Download materialsEvaluating
See the product live.
Talk to an expert